Using the previous firmware could lead to problems with
PROTECTED_FENCE_SIGNAL commands, specifically causing register
conflicts between MCU_DBG0 and MCU_DBG1.

The updated firmware versions ensure proper alignment
and unification of the SDMA_SUBOP_PROTECTED_FENCE_SIGNAL value with SDMA 7.x,
resolving these hardware coordination issues

Fixes: e8cca30d8b ("drm/amdgpu/sdma6: add ucode version checks for userq support")
Acked-by: Alex Deucher <alexander.deucher@amd.com>
Signed-off-by: Jesse Zhang <Jesse.Zhang@amd.com>
Signed-off-by: Alex Deucher <alexander.deucher@amd.com>
(cherry picked from commit aab8b689ad)
Cc: stable@vger.kernel.org
Signed-off-by: Carlos Maiolino <cem@kernel.org>
 -----BEGIN PGP SIGNATURE-----

 iJUEABMJAB0WIQSmtYVZ/MfVMGUq1GNcsMJ8RxYuYwUCaLGSlwAKCRBcsMJ8RxYu
 Y+uuAYCkjWybzYLQmsNuae2WVa1s0O8soCt/DBxlIvgALPIZx54MbMCXYHK4/0US
 gZWDBPwBgLxYoCoqEIbVkZXJA9DU8UjFCAyKGBbjR7n5ygJGU/I5uwJAWbdeDP21
 8lqxPxx2ng==
 =GUea
 -----END PGP SIGNATURE-----

Merge tag 'xfs-fixes-6.17-rc4' of git://git.kernel.org/pub/scm/fs/xfs/xfs-linux

Pull xfs fixes from Carlos Maiolino:
 "The highlight I'd like to point here is related to the XFS_RT
  Kconfig, which has been updated to be enabled by default now if
  CONFIG_BLK_DEV_ZONED is enabled.

  This also contains a few fixes for zoned devices support in XFS,
  specially related to swapon requests in inodes belonging to the zoned
  FS.

  A null-ptr dereference fix in the xattr data, due to a mishandling of
  medium errors generated by block devices is also included"

* tag 'xfs-fixes-6.17-rc4' of git://git.kernel.org/pub/scm/fs/xfs/xfs-linux:
  xfs: do not propagate ENODATA disk errors into xattr code
  xfs: reject swapon for inodes on a zoned file system earlier
  xfs: kick off inodegc when failing to reserve zoned blocks
  xfs: remove xfs_last_used_zone
  xfs: Default XFS_RT to Y if CONFIG_BLK_DEV_ZONED is enabled
-----BEGIN PGP SIGNATURE-----

 iQIzBAABCAAdFiEEL65usyKPHcrRDEicpmLzj2vtYEkFAmixtiMACgkQpmLzj2vt
 YEkMhBAAmpdDXi5YyUkU+8qwZpIfPHUR9k+pv6vIfcALNZVy1siaspwZvWdX4GHw
 ghxQoH/L84rN6bhiHBG/8FrX2TUNizstQro6/wDc4G2EcXde9h0/SZOqqUaszR51
 1O09ns4Po9UI4ekHepx9vrCk+mSDDTRTptw0ALSo/RvqtnzeoCR+7EfGRjAVOY+z
 K2yEk5c6rmYocARHqmNrOWQEiUA94seLjCjKKkJdkzRRb3o9NU+uj1uixIlDsIIh
 SpxG/c1fqPxETOX+JNMm9L/7PQkTrMigdwtlTxvimj1CFXZtOMB6gDo4V1Qc5kuH
 yGcgfr+3mO1u3hfQ43nowz9Fuxrnru3qanP9TvY1/uBE+HPuXr4Nz09KEmJAC61l
 NBz3CqapCAo2tMA+BWHlmjdf3WufwlMQerVSipx0tn5ULfx7qJk3Nn1y4toef3qb
 9tDoN/tbFMA/IEfUwe/eHRFy4/Z5YgS7H/mTPp9UEtM0r/MwONwBSuGehY1dV2M9
 O9gNoUog8h3NbGbGLy9Fkb+c2Q9wXh4ISkvxJmfRBUJQemGxzEjTOhqk0jUalzo4
 AwhpE/BqPNb8dm52PhjZjXLefah8J03sZXN6TIpAS5vuDI9P97Ypa7Z6UGDjB4ao
 289r5xLsMRaUV6swTZNcgYoYj5oSEmpHNxody53W9v0Hn5ZjL7s=
 =WR2w
 -----END PGP SIGNATURE-----

Merge tag 'hid-for-linus-2025082901' of git://git.kernel.org/pub/scm/linux/kernel/git/hid/hid

Pull HID fixes from Jiri Kosina:

 - fixes for memory corruption in intel-thc-hid, hid-multitouch,
   hid-mcp2221 and hid-asus (Aaron Ma, Qasim Ijaz, Arnaud Lecomte)

 - power management/resume fix for intel-ish-hid (Zhang Lixu)

 - driver reinitialization fix for intel-thc-hid (Even Xu)

 - ensure that battery level status is reported as soon as possible,
   which is required at least for some Android use-cases (José Expósito)

 - quite a few new device ID additions and device-specific quirks

* tag 'hid-for-linus-2025082901' of git://git.kernel.org/pub/scm/linux/kernel/git/hid/hid:
  HID: quirks: add support for Legion Go dual dinput modes
  HID: elecom: add support for ELECOM M-DT2DRBK
  HID: logitech: Add ids for G PRO 2 LIGHTSPEED
  HID: input: report battery status changes immediately
  HID: input: rename hidinput_set_battery_charge_status()
  HID: intel-thc-hid: Intel-quicki2c: Enhance driver re-install flow
  HID: hid-ntrig: fix unable to handle page fault in ntrig_report_version()
  HID: asus: fix UAF via HID_CLAIMED_INPUT validation
  hid: fix I2C read buffer overflow in raw_event() for mcp2221
  HID: wacom: Add a new Art Pen 2
  HID: multitouch: fix slab out-of-bounds access in mt_report_fixup()
  HID: Kconfig: Fix spelling mistake "enthropy" -> "entropy"
  HID: intel-ish-hid: Increase ISHTP resume ack timeout to 300ms
  HID: intel-thc-hid: intel-thc: Fix incorrect pointer arithmetic in I2C regs save
  HID: intel-thc-hid: intel-quicki2c: Fix ACPI dsd ICRS/ISUB length
One simple fix for the pm8008 driver for poor error handling, switching
 to use a helper which does the right thing in the affected case.
 -----BEGIN PGP SIGNATURE-----

 iQEzBAABCgAdFiEEreZoqmdXGLWf4p/qJNaLcl1Uh9AFAmixZ7EACgkQJNaLcl1U
 h9DyDQf+PQZvcoEVFedJqvPaE4mF0FotAqDphgptJ69qY2hXzKu/W9QrUnR+I6CC
 YSf4keEM7qhMVP+rFXOmz0/rQLzoWJRui4PlQ4NdDpzW0pRw1zRCHeAZp4o1FpbW
 eozsSqSiJdXWUANtTgPpoCxGQvPMVfs2WNoBrGxp0yBeAhQD3R54cAfcEdvWKA/F
 rOz310Q70eQhLzGc4n7FKJ/uG/V9sT+J+nDFGyOuO7qvHjTahfYnlSyUqULbb9qU
 qMA0w8Xk95JwO0SM/2XMGAj0F7TR3RvyMQ4wBrOjV4vSdjNRCPBHVySFCAQDBL1D
 QFAclZyqr7qUTOnLjCeTbMmZKBX5YA==
 =oR0J
 -----END PGP SIGNATURE-----

Merge tag 'regulator-fix-v6.17-rc3' of git://git.kernel.org/pub/scm/linux/kernel/git/broonie/regulator

Pull regulator fix from Mark Brown:
 "One simple fix for the pm8008 driver for poor error handling,
  switching to use a helper which does the right thing in the
  affected case"

* tag 'regulator-fix-v6.17-rc3' of git://git.kernel.org/pub/scm/linux/kernel/git/broonie/regulator:
  regulator: pm8008: fix probe failure due to negative voltage selector
- Fix the type of return values to be signed in the ahci_xgen driver
    (Qianfeng).

  - Add the mask_port_ext module parameter to the ahci driver. This is to
    allow a user to ignore ports that are advertized as external (hotplug
    capable) in favor of lower link power management policies instead of
    the default max_performance for these ports. This is useful to allow
    e.g. laptops to go into low power states when hooked up to docking
    station with sata slots, connected with an external port for hotplug
    (me).
 -----BEGIN PGP SIGNATURE-----

 iHUEABYKAB0WIQSRPv8tYSvhwAzJdzjdoc3SxdoYdgUCaLFeigAKCRDdoc3SxdoY
 dowvAP9Ui0ymEcYwOsuYDX2APDqe8B9+KJMkNLeRMbZdkK5zlAD/dVB/wxQNolOU
 UaYSYfRXHBjcoTI6jmxhOlXkryIvBAo=
 =iGob
 -----END PGP SIGNATURE-----

Merge tag 'ata-6.17-rc4' of git://git.kernel.org/pub/scm/linux/kernel/git/libata/linux

Pull ata fixes from Damien Le Moal:

 - Fix the type of return values to be signed in the ahci_xgen driver
   (Qianfeng)

 - Add the mask_port_ext module parameter to the ahci driver.

   This is to allow a user to ignore ports that are advertized as
   external (hotplug capable) in favor of lower link power management
   policies instead of the default max_performance for these ports.

   This is useful to allow e.g. laptops to go into low power states when
   hooked up to docking station with sata slots, connected with an
   external port for hotplug (me)

* tag 'ata-6.17-rc4' of git://git.kernel.org/pub/scm/linux/kernel/git/libata/linux:
  ata: ahci_xgene: Use int type for 'rc' to store error codes
  ata: ahci: Allow ignoring the external/hotplug capability of ports
ina238_write_temp() was attempting to clamp the user input but was
throwing away the result. Ensure that we clamp the value to the
appropriate range before it is converted into a register value.

Fixes: 0d9f596b1f ("hwmon: (ina238) Modify the calculation formula to adapt to different chips")
Signed-off-by: Chris Packham <chris.packham@alliedtelesis.co.nz>
Link: https://lore.kernel.org/r/20250829030512.1179998-3-chris.packham@alliedtelesis.co.nz
Signed-off-by: Guenter Roeck <linux@roeck-us.net>
The fans controlled by the driver can get stuck at 0 RPM if they are
configured below a 20% duty cycle. The driver tries to avoid this by
enforcing a minimum duty cycle of 20%, but this is done after the fans
are registered with the thermal subsystem. This is too late as the
thermal subsystem can set their current state before the driver is able
to enforce the minimum duty cycle.

Fix by setting the minimum duty cycle before registering the fans with
the thermal subsystem.

Fixes: d7efb2ebc7 ("hwmon: (mlxreg-fan) Extend driver to support multiply cooling devices")
Reported-by: Nikolay Aleksandrov <razor@blackwall.org>
Tested-by: Nikolay Aleksandrov <razor@blackwall.org>
Signed-off-by: Ido Schimmel <idosch@nvidia.com>
Signed-off-by: Vadim Pasternak <vadimp@nvidia.com>
Link: https://lore.kernel.org/r/20250730201715.1111133-1-vadimp@nvidia.com
Signed-off-by: Guenter Roeck <linux@roeck-us.net>
Currently, tpmi_get_logical_id() calls topology_physical_package_id()
to set the pkg_id of the info structure. Since some VM hosts assign non
contiguous package IDs, topology_physical_package_id() can return a
larger value than topology_max_packages(). This will result in an
invalid reference into tpmi_power_domain_mask[] as that is allocatead
based on topology_max_packages() as the maximum package ID.

Fixes: 17ca278045 ("platform/x86/intel: TPMI domain id and CPU mapping")
Signed-off-by: David Arcari <darcari@redhat.com>
Acked-by: Srinivas Pandruvada <srinivas.pandruvada@linux.intel.com>
Link: https://lore.kernel.org/r/20250829113859.1772827-1-darcari@redhat.com
Reviewed-by: Ilpo Järvinen <ilpo.jarvinen@linux.intel.com>
Signed-off-by: Ilpo Järvinen <ilpo.jarvinen@linux.intel.com>
In commit 1352964774 ("spi: microchip-core-qspi: Support per spi-mem
operation frequency switches") the logic for checking the viability of
op->max_freq in mchp_coreqspi_setup_clock() was copied into
mchp_coreqspi_supports_op(). Unfortunately, op->max_freq is not valid
when this function is called during probe but is instead zero.
Accordingly, baud_rate_val is calculated to be INT_MAX due to division
by zero, causing probe of the attached memory device to fail.

Seemingly spi-microchip-core-qspi was the only driver that had such a
modification made to its supports_op callback when the per_op_freq
capability was added, so just remove it to restore prior functionality.

CC: stable@vger.kernel.org
Reported-by: Valentina Fernandez <valentina.fernandezalanis@microchip.com>
Fixes: 1352964774 ("spi: microchip-core-qspi: Support per spi-mem operation frequency switches")
Signed-off-by: Conor Dooley <conor.dooley@microchip.com>
Message-ID: <20250825-during-ploy-939bdd068593@spud>
Signed-off-by: Mark Brown <broonie@kernel.org>
The main fixes here are for some of the cleanups done in the core in
 this release, we had broken component lookup in the case with a single
 bus and DMA controller.  Otherwise it's driver specific changes, the
 shortlogs for the Intel WCL and rsnd drivers look like minor cleanups
 but are actually bugfixes (adding an op needed for correct functionality
 and reverting an inappropriate helper usage).
 -----BEGIN PGP SIGNATURE-----

 iQEzBAABCgAdFiEEreZoqmdXGLWf4p/qJNaLcl1Uh9AFAmixaaEACgkQJNaLcl1U
 h9DioQf+PKWlxGo/McqedxpEb3LvsOzY0UTgsWLLhNjfghS+9GdSFLtIclG6ekqe
 Cl3W0z5KJQcmiOyG9Uyr4OwyqfzTgggIhQ1t7ILSuI9Ogm2sQTF4c7UdbhkX6AUz
 IG841gzLVQA6Lo4qqceoEKvycNVndkGrkGSqEYEvrlhTxjlg1NycWMdiB+Yh6FqK
 8/ToiWPbRSYd9WlBttWgc0Luj433ErcNqhTvuXXC0R5milcVA3XpcStgWLfBHTXe
 qlZrWlTzBaqaT31fpEuFGzbjo1BqXjcqgofcpuyf6xBTjSvFQsqIr17yNHUtxz8P
 tgkLOs6ffclMviamcCAyLJsGzQ+d5A==
 =K12t
 -----END PGP SIGNATURE-----

Merge tag 'asoc-fix-v6.17-rc3' of https://git.kernel.org/pub/scm/linux/kernel/git/broonie/sound into for-linus

ASoC: Fixes for v6.17

The main fixes here are for some of the cleanups done in the core in
this release, we had broken component lookup in the case with a single
bus and DMA controller.  Otherwise it's driver specific changes, the
shortlogs for the Intel WCL and rsnd drivers look like minor cleanups
but are actually bugfixes (adding an op needed for correct functionality
and reverting an inappropriate helper usage).
Applying the quirk of that, the lowest Playback mixer volume setting
mutes the audio output, on more devices.

Suggested-by: Cryolitia PukNgae <cryolitia@uniontech.com>
Signed-off-by: qaqland <anguoli@uniontech.com>
Link: https://patch.msgid.link/20250829-sound_quirk-v1-1-745529b44440@uniontech.com
Signed-off-by: Takashi Iwai <tiwai@suse.de>
Commit 620c266f39 ("fhandle: relax open_by_handle_at() permission
checks") relaxed the coditions for decoding a file handle from non init
userns.

The conditions are that that decoded dentry is accessible from the user
provided mountfd (or to fs root) and that all the ancestors along the
path have a valid id mapping in the userns.

These conditions are intentionally more strict than the condition that
the decoded dentry should be "lookable" by path from the mountfd.

For example, the path /home/amir/dir/subdir is lookable by path from
unpriv userns of user amir, because /home perms is 755, but the owner of
/home does not have a valid id mapping in unpriv userns of user amir.

The current code did not check that the decoded dentry itself has a
valid id mapping in the userns.  There is no security risk in that,
because that final open still performs the needed permission checks,
but this is inconsistent with the checks performed on the ancestors,
so the behavior can be a bit confusing.

Add the check for the decoded dentry itself, so that the entire path,
including the last component has a valid id mapping in the userns.

Fixes: 620c266f39 ("fhandle: relax open_by_handle_at() permission checks")
Signed-off-by: Amir Goldstein <amir73il@gmail.com>
Link: https://lore.kernel.org/20250827194309.1259650-1-amir73il@gmail.com
Signed-off-by: Christian Brauner <brauner@kernel.org>
gpuvm:
 - fix some typos

 xe:
 - Fix user-fence race issue
 - Couple xe_vm fixes
 - Don't trigger rebind on initial dma-buf validation
 - Fix a build issue related to basename() posix vs gnu discrepancy

 amdgpu:
 - pin buffers while vmapping
 - UserQ fixes
 - Revert CSA fix
 - SR-IOV fix

 nouveau:
 - fix linear modifier
 - remove some dead code

 msm:
 - Core/GPU:
   - fix comment doc warning in gpuvm
   - fix build with KMS disabled
   - fix pgtable setup/teardown race
   - global fault counter fix
   - various error path fixes
   - GPU devcoredump snapshot fixes
   - handle in-place VM_BIND remaps to solve turnip vm update race
   - skip re-emitting IBs for unusable VMs
   - Don't use %pK through printk
   - moved display snapshot init earlier, fixing a crash
 - DPU:
   - Fixed crash in virtual plane checking code
   - Fixed mode comparison in virtual plane checking code
 - DSI:
   - Adjusted width of resulution-related registers
   - Fixed locking issue on 14nm PLLs
 - UBWC (per Bjorn's ack)
   - Added UBWC configuration for several missing platforms (fixing
     regression)

 mediatek:
 - Add error handling for old state CRTC in atomic_disable
 - Fix DSI host and panel bridge pre-enable order
 - Fix device/node reference count leaks in mtk_drm_get_all_drm_priv
 - mtk_hdmi: Fix inverted parameters in some regmap_update_bits calls

 tegra:
 - revert dma-buf change
 -----BEGIN PGP SIGNATURE-----

 iQIzBAABCgAdFiEEEKbZHaGwW9KfbeusDHTzWXnEhr4FAmixFPQACgkQDHTzWXnE
 hr4d4Q/+Lf/meDiKrjUHiNwW+kZPeZhwrKEEbG2Opc9uZZdQpx44ZhOKM668dUx1
 YWAC2hcQFKWe0tz4Qsg2drPBGmoobhxmVScwXpY7xz1XN4taINssuZRwERp3bLmx
 l63tcQleGJOYvbCcg0SCfDeR4fd7a7iVf+PelFU04mbn/qorJBdYuy/XPTZlCond
 lf1MtaPH8f2M80WHmwb4g5K3mIdIa0HCt6Z9Z73mLRmF0b6KfcWF8159OLz03tiS
 voHDmFR4VsoZihDC4H+fAAitbQG+5vZN6YtX2CC4OtQLxeGkpkOniGwfjD/beKne
 edGHvWpzBchmK0Z6o64+7rzJa7RYEkpgryvAD/jEljG9kk0RzlGAYvXFV3aeLFLn
 +WJX8ZOw/SqkGX5/DDA0CpDb3Ty8QxEmS/MEHn/kAUNmBp0Uw2ad6b/4b3NqkDh9
 ftgWSobFubZJ8oSf8amPwpW7KjSsccogQzASiuDlV/XCCdlKvuxkn/ZX9XjHq0rr
 O0CX+4vLhl20grRstD4oIVsmrLYQXg97uqpOeaoMrzflKfyEzJ7bxDSBd78ZbfVf
 dlHSULx3cgusNe8HNWRnsnC0XeC1MBTXCbpTjrZYkqu1arLZN+r8LXOGRZrKBCPu
 PtlmU21JJKygKUTWeXzX1P2eBdBoTloOKJGkLWthR9KxFDqfppM=
 =QtCr
 -----END PGP SIGNATURE-----

Merge tag 'drm-fixes-2025-08-29' of https://gitlab.freedesktop.org/drm/kernel

Pull drm fixes from Dave Airlie:
 "Weekly fixes, feels a bit big.

  The major piece is msm fixes, then the usual amdgpu/xe along with some
  mediatek and nouveau fixes and a tegra revert.

  gpuvm:
   - fix some typos

  xe:
   - Fix user-fence race issue
   - Couple xe_vm fixes
   - Don't trigger rebind on initial dma-buf validation
   - Fix a build issue related to basename() posix vs gnu discrepancy

  amdgpu:
   - pin buffers while vmapping
   - UserQ fixes
   - Revert CSA fix
   - SR-IOV fix

  nouveau:
   - fix linear modifier
   - remove some dead code

  msm:
   - Core/GPU:
      - fix comment doc warning in gpuvm
      - fix build with KMS disabled
      - fix pgtable setup/teardown race
      - global fault counter fix
      - various error path fixes
      - GPU devcoredump snapshot fixes
      - handle in-place VM_BIND remaps to solve turnip vm update race
      - skip re-emitting IBs for unusable VMs
      - Don't use %pK through printk
      - moved display snapshot init earlier, fixing a crash
   - DPU:
      - Fixed crash in virtual plane checking code
      - Fixed mode comparison in virtual plane checking code
   - DSI:
      - Adjusted width of resulution-related registers
      - Fixed locking issue on 14nm PLLs
   - UBWC (per Bjorn's ack)
      - Added UBWC configuration for several missing platforms (fixing
        regression)

  mediatek:
   - Add error handling for old state CRTC in atomic_disable
   - Fix DSI host and panel bridge pre-enable order
   - Fix device/node reference count leaks in mtk_drm_get_all_drm_priv
   - mtk_hdmi: Fix inverted parameters in some regmap_update_bits calls

  tegra:
   - revert dma-buf change"

* tag 'drm-fixes-2025-08-29' of https://gitlab.freedesktop.org/drm/kernel: (56 commits)
  drm/mediatek: mtk_hdmi: Fix inverted parameters in some regmap_update_bits calls
  drm/amdgpu/userq: fix error handling of invalid doorbell
  drm/amdgpu: update firmware version checks for user queue support
  drm/amd/amdgpu: disable hwmon power1_cap* for gfx 11.0.3 on vf mode
  Revert "drm/amdgpu: fix incorrect vm flags to map bo"
  drm/amdgpu/gfx12: set MQD as appriopriate for queue types
  drm/amdgpu/gfx11: set MQD as appriopriate for queue types
  drm/xe: switch to local xbasename() helper
  drm/xe: Don't trigger rebind on initial dma-buf validation
  drm/xe/vm: Clear the scratch_pt pointer on error
  drm/xe/vm: Don't pin the vm_resv during validation
  drm/xe/xe_sync: avoid race during ufence signaling
  Revert "drm/tegra: Use dma_buf from GEM object instance"
  soc: qcom: use no-UBWC config for MSM8956/76
  soc: qcom: add configuration for MSM8929
  soc: qcom: ubwc: add more missing platforms
  soc: qcom: ubwc: use no-uwbc config for MSM8917
  drm/msm/dpu: Add a null ptr check for dpu_encoder_needs_modeset
  dt-bindings: display/msm: qcom,mdp5: drop lut clock
  drm/gpuvm: fix various typos in .c and .h gpuvm file
  ...
-----BEGIN PGP SIGNATURE-----

 iQJEBAABCAAuFiEEwPw5LcreJtl1+l5K99NY+ylx4KYFAmiwwhkQHGF4Ym9lQGtl
 cm5lbC5kawAKCRD301j7KXHgpnooD/92QqpW1IOn0hs0WGOiKl7se5JgBuLV9bd0
 j7M8EpGyFK63zeDgAO0/Qu2arEva9tlDaW9S/e78kt1PwQ7it82RSlPC47nKWEv+
 Xn5npn2SOEkyY/5/a+iVkOsSD++RIM/DnHNBe9vmU6wePR7AthG5Nhl6kOEi5cyw
 e1eLbwB/0eJZzhHYCaowLwdtnMCcwQAEh/FFYz7tSyrgOsDpovKid6D7s2Sv9sGA
 +lOzwimgszr3RF5bOMudU12RtP35gAvyF56iDVMQylHXybuaYYzzVAmxRLD5vrOf
 vC4HSzRxwUCZnIW62TTP29dAB9mik3va069e1xV1le94vdEsgj2HmuV4tpCzs3LN
 4a1q8oEC83QI+cixzsjxf00DaJSkk9msUNsqE+6rcEK0M6z0tRz3mbLXYiCo7V4Y
 eLD7eMsxXkJUSpTwWOIVYiXuM+OvSmFxIEoz4lGnQESKyV0dA86RT5TpOiUCrkW1
 G9nTccxVPZG3i8FKJXmgZLPmpviw+wwzdpjlVShqSGA++/bBXKwAnjAQPSsaVDIS
 HaqhG1IngL9sCcnAy8ZBTEy2TYibasUL48vfCeRhP2u2RZa21zRSOPNFRV9cVvRE
 /wOWQikOqC9ys7zvbLG0OfLQAlejGn1k+k6oEOI6P9x2a0vbjq/UZxIQSkdYEhXG
 x73gWYk28g==
 =/1eG
 -----END PGP SIGNATURE-----

Merge tag 'block-6.17-20250828' of git://git.kernel.dk/linux

Pull block fixes from Jens Axboe:

 - Fix a lockdep spotted issue on recursive locking for zoned writes, in
   case of errors

 - Update bcache MAINTAINERS entry address for Coly

 - Fix for a ublk release issue, with selftests

 - Fix for a regression introduced in this cycle, where it assumed
   q->rq_qos was always set if the bio flag indicated that

 - Fix for a regression introduced in this cycle, where loop retrieving
   block device sizes got broken

* tag 'block-6.17-20250828' of git://git.kernel.dk/linux:
  bcache: change maintainer's email address
  ublk selftests: add --no_ublk_fixed_fd for not using registered ublk char device
  ublk: avoid ublk_io_release() called after ublk char dev is closed
  block: validate QoS before calling __rq_qos_done_bio()
  blk-zoned: Fix a lockdep complaint about recursive locking
  loop: fix zero sized loop for block special file
-----BEGIN PGP SIGNATURE-----

 iQJEBAABCAAuFiEEwPw5LcreJtl1+l5K99NY+ylx4KYFAmiwwi8QHGF4Ym9lQGtl
 cm5lbC5kawAKCRD301j7KXHgpvBdD/4lwnluUoyPn7pm6QMNG7oGn4ix7drP797P
 TfOFgQHSepBq8VqEKE+B3dA4n+rCMFy601psaG9pQW9R0pDWHN3FG+TkaQl6ixdS
 t18q/JXbzIiD4aTD9Dz/dkkY6EczIPFqVwg+Lc4K89P3vNri70lHXXmDTlbumB3P
 PIkxU7PvueO6dZf79QjdczxDw6I5lUJJv6iAn6H6EMy5gJVF01rZqbSl3i08kSVQ
 6i26rEw0QkzC30SzU2m5H5qrdD8OewG6Fr5zwiNbCuqLdZBgvzqPR25WeSNRHV5F
 CF23QImuQwBnrHloDPI7Uvz0yC6W3jNIW+nF6X5SV1U51BMZ1ED5hQZczRoJpmco
 1Vhz7tanPa1qNrNeu7E7vfHuQ/gIKnjgXptLRTL+4HRk65TZpXcS5b2vJsAZf32x
 nYIaYjxUmGCayQgAE8tqXvfsmzLQ0BbvZMr45lm32uVbesDZh9Vp9q10BetsmQEk
 f17qjJz6weYUnO1fktRWLUtHZVbNeuf5VLalRod/FOBVo9J84XC4JebjN/X4FGWY
 +2GIepX5LnrI/2xSaAbJURIj0TL6wSnmu/H3RoGLDvAvMC7atqHSt9TMBNIdYhNY
 u6ez5Jd/tYM/bW3WUtFLRqtjVJ8uxtAAEeiGxtyuscS7EL0KgRBnygls0om7plUa
 hCQbB/lnOA==
 =KXyz
 -----END PGP SIGNATURE-----

Merge tag 'io_uring-6.17-20250828' of git://git.kernel.dk/linux

Pull io_uring fixes from Jens Axboe:

 - Use the proper type for min_t() in getting the min of the leftover
   bytes and the buffer length.

 - As good practice, use READ_ONCE() consistently for reading ring
   provided buffer lengths. Additionally, stop looping for incremental
   commits if a zero sized buffer is hit, as no further progress can be
   made at that point.

* tag 'io_uring-6.17-20250828' of git://git.kernel.dk/linux:
  io_uring/kbuf: always use READ_ONCE() to read ring provided buffer lengths
  io_uring/kbuf: fix signedness in this_len calculation
1. Add error handling for old state CRTC in atomic_disable
 2. Fix DSI host and panel bridge pre-enable order
 3. Fix device/node reference count leaks in mtk_drm_get_all_drm_priv
 4. mtk_hdmi: Fix inverted parameters in some regmap_update_bits calls
 -----BEGIN PGP SIGNATURE-----

 iQJMBAABCgA2FiEEACwLKSDmq+9RDv5P4cpzo8lZTiQFAmiw5k4YHGNodW5rdWFu
 Zy5odUBrZXJuZWwub3JnAAoJEOHKc6PJWU4klDcP+wXMw/9gEBq7JTaFs9dvtvf7
 yXZdoSAmTVgjYT3gArC98kXBA6mbRvKkG4s6M2uJuczVml+6mxarwsLkfFIiRiSB
 Nk9lhV84WKdqvSRcVyYuI47Pkp1QR3yPX7UD9OCm9iq+VjQeHNhIxR5GLZ0Rt8wR
 5OST60KoNHBH9jWMn9GbWh1FYtqtdvcOWr90ZtKvsyPXyHVXfqsoDy8PJ9X+vwJq
 sbgdO2BRd7jEJ8+tcI4ZOJl1x6+Q3RXosYzcxvIXtrDr39ETKLFiloL9o7H27rSU
 z6G1xyGo1dOMQ3LGMYQMr0QziqVPVPBDmrd2cv/Nf1yeCCy1E+msqpm0u6vcOJ2x
 Soq/zaPUMut5VaHKfIpFOCiKiIKhcxlP5krYg3g4rg4JzxHzCUCfawblQrleNDJx
 FUUmHxjELPfuUDbPdAWoq33UVbuUNYpDseSbrGbskKA+gzcYQtwNElae8283fC5H
 47W8y1UmwOutbnoTcVW7RRl2RAbjXjjID6tRtbVGHWS5ST5NnxFbcRX1uwzDoC+3
 T2UCDYXDhJuhUKeahFfDjwMcvy8BcGqIqo3oqptcpr4hRvGPXaLVL7smWXOJNpgF
 qRmN8bbNZjgQlHHdBYN7a9XKRK7nRNmRFtnE9FUQVOmbU7y5q90uOiy4qwZIMw1Q
 nmXAMvjQVfjCbemvU6ad
 =j/Jq
 -----END PGP SIGNATURE-----

Merge tag 'mediatek-drm-fixes-20250829' of https://git.kernel.org/pub/scm/linux/kernel/git/chunkuang.hu/linux into drm-fixes

Mediatek DRM Fixes - 20250829

1. Add error handling for old state CRTC in atomic_disable
2. Fix DSI host and panel bridge pre-enable order
3. Fix device/node reference count leaks in mtk_drm_get_all_drm_priv
4. mtk_hdmi: Fix inverted parameters in some regmap_update_bits calls

Signed-off-by: Dave Airlie <airlied@redhat.com>

From: Chun-Kuang Hu <chunkuang.hu@kernel.org>
Link: https://lore.kernel.org/r/20250828234116.4960-1-chunkuang.hu@kernel.org
Add missing locking annotations to two recently introduced
 list_for_each_entry_rcu() loops in the core device suspend/resume
 code (Johannes Berg)
 -----BEGIN PGP SIGNATURE-----

 iQFGBAABCAAwFiEEcM8Aw/RY0dgsiRUR7l+9nS/U47UFAmiws2ESHHJqd0Byand5
 c29ja2kubmV0AAoJEO5fvZ0v1OO1hSIIAI8UeQnihDtPYR0bklyzENW/g17Du/4M
 UZPxd50YB4xSofLhHDZCf214Yg5vihV3Hdj51XkDn+Wyd2HTYC5GW/qLcUL9gpLj
 MflA6O0ZtYpAE3bByK+XI4Wwas05h/LuF63ty8i+2zrS7NV7EaFa1+3Hj7wgQ7wZ
 QGsaTdet3kxgJa/KbLOkzXayrLiAk4OtrFpABu+8cjzHi1wDg8on00+zW1FN5b9U
 f14jsdds+as1usw6Gf8lSSUgtLNQ/kQ41Btg2naG4B6TD9N9WpVwkx1TCrXcDj2E
 Wff/dTSfBU8As8D9ZPr4HOk9tmFmdwcFareT4wRBljbys6ixgYvxGX8=
 =9Avh
 -----END PGP SIGNATURE-----

Merge tag 'pm-6.17-rc4' of git://git.kernel.org/pub/scm/linux/kernel/git/rafael/linux-pm

Pull power management fix from Rafael Wysocki:
 "Add missing locking annotations to two recently introduced
  list_for_each_entry_rcu() loops in the core device suspend/resume
  code (Johannes Berg)"

* tag 'pm-6.17-rc4' of git://git.kernel.org/pub/scm/linux/kernel/git/rafael/linux-pm:
  PM: sleep: annotate RCU list iterations
In mtk_hdmi driver, a recent change replaced custom register access
function calls by regmap ones, but two replacements by regmap_update_bits
were done incorrectly, because original offset and mask parameters were
inverted, so fix them.

Fixes: d6e25b3590 ("drm/mediatek: hdmi: Use regmap instead of iomem for main registers")
Signed-off-by: Louis-Alexis Eyraud <louisalexis.eyraud@collabora.com>
Reviewed-by: CK Hu <ck.hu@mediatek.com>
Link: https://patchwork.kernel.org/project/dri-devel/patch/20250818-mt8173-fix-hdmi-issue-v1-1-55aff9b0295d@collabora.com/
Signed-off-by: Chun-Kuang Hu <chunkuang.hu@kernel.org>
- another small fix relevant to arm64 systems with memory encryption
 (Shanker Donthineni)
 - fix relevant to arm32 systems with non-standard CMA configuration
 (Oreoluwa Babatunde)
 -----BEGIN PGP SIGNATURE-----

 iHUEABYIAB0WIQSrngzkoBtlA8uaaJ+Jp1EFxbsSRAUCaLAK7gAKCRCJp1EFxbsS
 REDxAQC+5hLiyzc/1rR5EQb1D6Xr1f/0VN3IFz3creHp3juFBAEApi1iFMdmahO7
 0YKG4KkzHpcNkGrxaXKP0VNtQsDLwww=
 =fVrB
 -----END PGP SIGNATURE-----

Merge tag 'dma-mapping-6.17-2025-08-28' of git://git.kernel.org/pub/scm/linux/kernel/git/mszyprowski/linux

Pull dma-mapping fixes from Marek Szyprowski:

 - another small fix for arm64 systems with memory encryption (Shanker
   Donthineni)

 - fix for arm32 systems with non-standard CMA configuration (Oreoluwa
   Babatunde)

* tag 'dma-mapping-6.17-2025-08-28' of git://git.kernel.org/pub/scm/linux/kernel/git/mszyprowski/linux:
  dma/pool: Ensure DMA_DIRECT_REMAP allocations are decrypted
  of: reserved_mem: Restructure call site for dma_contiguous_early_fixup()
* printk cleanups in memblock and numa_memblks
 * update kernel-doc for MEMBLOCK_RSRV_NOINIT to be more accurate and
   detailed
 -----BEGIN PGP SIGNATURE-----

 iQFEBAABCgAuFiEEeOVYVaWZL5900a/pOQOGJssO/ZEFAmiv6AwQHHJwcHRAa2Vy
 bmVsLm9yZwAKCRA5A4Ymyw79kR4SB/4u5L2tlpZaM2PzMqHVrdXDWNs7ntmRr97e
 BA0fsIoSVtcqAEUkXiG+2x9cBuzJuiGOkSKOu28u7567zQji8rX3IAHaR1Uw1K+0
 2mmzC3QxMjM6g7g310uA+agMAQlZne6ppiCEqyNnng3Uda8zZudL8NojOjtr3rJi
 +ebiy5/2KR9DDV+758ZCQ4MmBGqnS5YLXu+xXbmnsPw7AqujSADskvrTLugii5qp
 khQwTEX9foUR9kwAsrHPmqW560m2oWNf4eh3uxWtVxuCtbAnqC6uxVnaORW7UKaB
 gLcOCinvBE6Le4sggJQvr6NpAJ1HcrXzA61CfBV9UUXNXb9obxDO
 =xp5F
 -----END PGP SIGNATURE-----

Merge tag 'fixes-2025-08-28' of git://git.kernel.org/pub/scm/linux/kernel/git/rppt/memblock

Pull memblock fixes from Mike Rapoport:

 - printk cleanups in memblock and numa_memblks

 - update kernel-doc for MEMBLOCK_RSRV_NOINIT to be more accurate and
   detailed

* tag 'fixes-2025-08-28' of git://git.kernel.org/pub/scm/linux/kernel/git/rppt/memblock:
  memblock: fix kernel-doc for MEMBLOCK_RSRV_NOINIT
  mm: numa,memblock: Use SZ_1M macro to denote bytes to MB conversion
  mm/numa_memblks: Use pr_debug instead of printk(KERN_DEBUG)
less restrictive with the formats it accepts. A fix for amdgpu to pin
 vmapped dma-buf, and a revert for tegra for a regression in the dma-buf
 / GEM code.
 -----BEGIN PGP SIGNATURE-----

 iJUEABMJAB0WIQTkHFbLp4ejekA/qfgnX84Zoj2+dgUCaK/35wAKCRAnX84Zoj2+
 duAqAX9IIovrilRa/6169LIVEFbI3NfhWJorjDp5GB6jEilKxu6LBWFNYmyiLLwI
 0+c4WiEBfAk/jHkpO4fdtAbIczic5d1WdSlO3VipH6w8WMDca1A3DcDM4BXO2x5Z
 74f5CctKSA==
 =PWA/
 -----END PGP SIGNATURE-----

Merge tag 'drm-misc-fixes-2025-08-28' of https://gitlab.freedesktop.org/drm/misc/kernel into drm-fixes

Several nouveau fixes to remove unused code, fix an error path and be
less restrictive with the formats it accepts. A fix for amdgpu to pin
vmapped dma-buf, and a revert for tegra for a regression in the dma-buf
/ GEM code.

Signed-off-by: Dave Airlie <airlied@redhat.com>

From: Maxime Ripard <mripard@redhat.com>
Link: https://lore.kernel.org/r/20250828-hypersonic-colorful-squirrel-64f04b@houat
- Merge two CONFIG_POWERPC64_CPU entries in Kconfig.cputype
  - Replace extra-y to always-y in Makefile
  - Cleanup to use dev_fwnode helper
  - Fix misleading comment in kvmppc_prepare_to_enter()
  - misc cleanup and fixes

 Thanks to: Amit Machhiwal, Andrew Donnellan, Christophe Leroy, Gautam Menghani,
 Jiri Slaby (SUSE), Masahiro Yamada, Shrikanth Hegde, Stephen Rothwell, Venkat
 Rao Bagalkote, Xichao Zhao
 -----BEGIN PGP SIGNATURE-----

 iQIzBAABCgAdFiEEqX2DNAOgU8sBX3pRpnEsdPSHZJQFAmiv5qEACgkQpnEsdPSH
 ZJQeEA/+NahRLWuQM/dikXUo/Nje0/VSuQn4t/Yw8SUpqteBmGw84r8VZkxY0yu4
 9Mmvi/7flStL59Nede94dEO7TJvOhcn7OD2X0gQpQl5ZaHD3z8oGmEnZ023tUin1
 kzuEtsRTepU2ELEpqJCGzGNxV+Sxv+pqP7Okg65/u9HCUaq/1e89J5Km4rw4svx4
 LLcs+FUAobbI7LV6SeKr877Ujp0dsLkSwvC/g4aqgszm4HbJi8WiD8QfTJYmzi6L
 f4VzCzl+ox1ml+IpQKbQfjbAiB4MCIHc1mMCuK+A4VFmqGnlqk4/oeUmrNanRwSR
 tDpeTka0HGO6dOIuf/G/Bc9bf23+dvKrH6NDpz4rI2mP88akedVMpLV9SmQXLZWy
 UEnLCf4Ic3DeVGvlwlXd6C+0wAqjqu3ud9I640mlJhGAdPJ+NR0XHDFKP3hgxh7o
 H8BQLBqm2CRDYOGFf8veY1u7EBsCTC0pjsvNrZa/IFzjOmZQJXwA4hG5sKkau3YG
 yOMzylhjpSPOPl85jaKS5XrIzXLYhFgZ13jqf3NNx6Ydmrg89tR+3RGvqG+H0pi2
 s/WQ+84Rw9hqzT7qOAQhUS1H7YHUOreeRrLZUVBl2SNXEh7Vw8ew1GkQJE7yMgsC
 8gfrnnomxaMtg0GnxdQEm7pb0rmBujWCc1QBA6pZdgDhE+M8U0Y=
 =+F44
 -----END PGP SIGNATURE-----

Merge tag 'powerpc-6.17-3' of git://git.kernel.org/pub/scm/linux/kernel/git/powerpc/linux

Pull powerpc fixes from Madhavan Srinivasan:

 - Merge two CONFIG_POWERPC64_CPU entries in Kconfig.cputype

 - Replace extra-y to always-y in Makefile

 - Cleanup to use dev_fwnode helper

 - Fix misleading comment in kvmppc_prepare_to_enter()

 - misc cleanup and fixes

Thanks to Amit Machhiwal, Andrew Donnellan, Christophe Leroy, Gautam
Menghani, Jiri Slaby (SUSE), Masahiro Yamada, Shrikanth Hegde, Stephen
Rothwell, Venkat Rao Bagalkote, and Xichao Zhao

* tag 'powerpc-6.17-3' of git://git.kernel.org/pub/scm/linux/kernel/git/powerpc/linux:
  powerpc/boot/install.sh: Fix shellcheck warnings
  powerpc/prom_init: Fix shellcheck warnings
  powerpc/kvm: Fix ifdef to remove build warning
  powerpc: unify two CONFIG_POWERPC64_CPU entries in the same choice block
  powerpc: use always-y instead of extra-y in Makefiles
  powerpc/64: Drop unnecessary 'rc' variable
  powerpc: Use dev_fwnode()
  KVM: PPC: Fix misleading interrupts comment in kvmppc_prepare_to_enter()
Volodymyr reports that using a Xen DomU as a nested guest (where
HCR_EL2.E2H == 0), ATS12 results in a translation that stops at
the L2's S1, which isn't something you'd normally expects.

Comparing the code against the spec proves to be illuminating,
and suggests that the author of such code must have been tired,
cross-eyed, drunk, or maybe all of the above.

The gist of it is that, apart from HCR_EL2.VM or HCR_EL2.DC being
0, only the use of the EL2&0 translation regime limits the walk
to S1 only, and that we must finish the S2 walk in any other case.
Which solves the above issue, as E2H==0 indicates that ATS12 walks
the EL1&0 translation regime.

Explicitly checking for EL2&0 fixes this.

Reported-by: Volodymyr Babchuk <volodymyr_babchuk@epam.com>
Suggested-by: Oliver Upton <oliver.upton@linux.dev>
Signed-off-by: Marc Zyngier <maz@kernel.org>
Fixes: be04cebf3e ("KVM: arm64: nv: Add emulation of AT S12E{0,1}{R,W}")
Link: https://lore.kernel.org/r/20250806141707.3479194-2-volodymyr_babchuk@epam.com
Link: https://lore.kernel.org/r/20250809144811.2314038-2-maz@kernel.org
Signed-off-by: Oliver Upton <oliver.upton@linux.dev>
Add the missing op in the device description to avoid issues with jack
detection.

Fixes: 6b04629ae9 ("ASoC: SOF: Intel: add initial support for WCL")
Acked-by: Peter Ujfalusi <peter.ujfalusi@linux.intel.com>
Signed-off-by: Ajye Huang <ajye_huang@compal.corp-partner.google.com>
Message-ID: <20250826154040.2723998-1-ajye_huang@compal.corp-partner.google.com>
Signed-off-by: Mark Brown <broonie@kernel.org>
There is no point having __vcpu_{read,write}_sys_reg_{from,to}_cpu()
exposed to the rest of the kernel, as the only callers are in
sys_regs.c.

Move them where they below, which is another opportunity to
simplify things a bit.

Signed-off-by: Marc Zyngier <maz@kernel.org>
Link: https://lore.kernel.org/r/20250817121926.217900-5-maz@kernel.org
Signed-off-by: Oliver Upton <oliver.upton@linux.dev>
Volodymyr reports (again!) that under some circumstances (E2H==0,
walking S1 PTs), PAR_EL1 doesn't report the value of the latest
walk in the CPU register, but that instead the value is written to
the backing store.

Further investigation indicates that the root cause of this is
that a group of registers (PAR_EL1, TPIDR*_EL{0,1}, the *32_EL2 dregs)
should always be considered as "on CPU", as they are not remapped
between EL1 and EL2.

We fail to treat them accordingly, and end-up considering that
the register (PAR_EL1 in this example) should be written to memory
instead of in the register.

While it would be possible to quickly work around it, it is obvious
that the way we track these things at the moment is pretty horrible,
and could do with some improvement.

Revamp the whole thing by:

- defining a location for a register (memory, cpu), potentially
  depending on the state of the vcpu

- define a transformation for this register (mapped register, potential
  translation, special register needing some particular attention)

- convey this information in a structure that can be easily passed
  around

As a result, the accessors themselves become much simpler, as the
state is explicit instead of being driven by hard-to-understand
conventions.

We get rid of the "pure EL2 register" notion, which wasn't very
useful, and add sanitisation of the values by applying the RESx
masks as required, something that was missing so far.

And of course, we add the missing registers to the list, with the
indication that they are always loaded.

Reported-by: Volodymyr Babchuk <volodymyr_babchuk@epam.com>
Signed-off-by: Marc Zyngier <maz@kernel.org>
Fixes: fedc612314 ("KVM: arm64: nv: Handle virtual EL2 registers in vcpu_read/write_sys_reg()")
Link: https://lore.kernel.org/r/20250806141707.3479194-3-volodymyr_babchuk@epam.com
Link: https://lore.kernel.org/r/20250817121926.217900-4-maz@kernel.org
Signed-off-by: Oliver Upton <oliver.upton@linux.dev>
Distinguishing between NV and VHE is slightly pointless, and only
serves as an extra complication, or a way to introduce bugs, such
as the way SPSR_EL1 gets written without checking for the state
being resident.

Get rid if this silly distinction, and fix the bug in one go.

Signed-off-by: Marc Zyngier <maz@kernel.org>
Link: https://lore.kernel.org/r/20250817121926.217900-3-maz@kernel.org
Signed-off-by: Oliver Upton <oliver.upton@linux.dev>
Just like c6e35dff58 ("KVM: arm64: Check for SYSREGS_ON_CPU before
accessing the CPU state") fixed the 64bit state access, add a check
for the 32bit state actually being on the CPU before writing it.

Signed-off-by: Marc Zyngier <maz@kernel.org>
Link: https://lore.kernel.org/r/20250817121926.217900-2-maz@kernel.org
Signed-off-by: Oliver Upton <oliver.upton@linux.dev>
For Intel SKL and KBL platforms, it may be bound with one of three
HD-audio drivers (AVS, SOF and legacy).  AVS is the preferred one when
DMIC is detected, and that's how it's defined in the snd-intel-dspcfg
config table.

But, when AVS driver is disabled (CONFIG_SND_SOC_INTEL_AVS=n), the
device may be bound freely with either SOF or legacy driver.
Before 6.17, the legacy driver took it primarily, but on 6.17, likely
due to the recent code shuffling, SOF driver seems taking it at first,
and fails to probe.  For avoiding the regression, we should enforce to
bind those with the legacy HD-audio drvier when AVS is disabled.

This patch adds the extra two entries in intel-dspcfg table that are
applied only when CONFIG_SND_SOC_INTEL_AVS=n, for binding with the
legacy driver.

Note that there are entries for APL in that config table block, but
APL may be supported by SOF for certain setups, so the choice can't be
exclusive.  Hence this patch includes only SKL and KBL.

Link: https://bugzilla.suse.com/show_bug.cgi?id=1248121
Reviewed-by: Cezary Rojewski <cezary.rojewski@intel.com>
Link: https://patch.msgid.link/20250828141101.16294-1-tiwai@suse.de
Signed-off-by: Takashi Iwai <tiwai@suse.de>
It turns out that the platform firmware on some models does not return
valid data when reading the bitmap of supported platform profiles.
This prevents the driver from loading on said models, even when the
platform profile interface itself works.

Fix this by stop using said bitmap until we have figured out how
the OEM software itself detects available platform profiles.

Tested-by: Lynne Megido <lynne@bune.city>
Reported-by: Lynne Megido <lynne@bune.city>
Closes: https://lore.kernel.org/platform-driver-x86/3f56e68f-85df-4c0a-982c-43f9d635be38@bune.city/
Fixes: 191e21f1a4 ("platform/x86: acer-wmi: use an ACPI bitmap to set the platform profile choices")
Signed-off-by: Armin Wolf <W_Armin@gmx.de>
Link: https://lore.kernel.org/r/20250826204007.5088-1-W_Armin@gmx.de
Reviewed-by: Ilpo Järvinen <ilpo.jarvinen@linux.intel.com>
Signed-off-by: Ilpo Järvinen <ilpo.jarvinen@linux.intel.com>
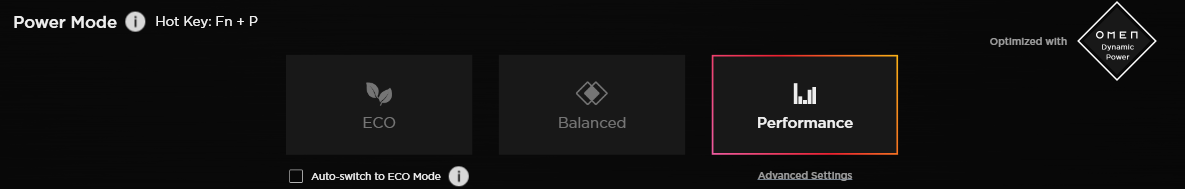
Add support for the Fn+P hotkey found on newer HP Victus (and probably
newer Omen) laptops. This hotkey is intended for use with Omen Gaming Hub
to change the performance profile (see [1]).

Pressing Fn+P under linux produced the following warning in dmesg:

> hp_wmi: Unknown event_id - 27 - 0x7

Implemented a handling for this event so that the hotkey cycles between the
platform profiles when triggered.

Tested on Victus 16-s1011nt (9Z791EA, MB 8C9C).

Changes in v2:
- Make the key just switches between platform profiles instead of
  assigning a key event code.
- v1: https://lore.kernel.org/all/20250802213541.18791-2-edip@medip.dev/

[1]: https://jpcdn.it/img/adadf6c927ffeb75afd8038f95db400a.png

Signed-off-by: Edip Hazuri <edip@medip.dev>
Link: https://lore.kernel.org/r/20250814204529.18467-4-edip@medip.dev
Reviewed-by: Ilpo Järvinen <ilpo.jarvinen@linux.intel.com>
Signed-off-by: Ilpo Järvinen <ilpo.jarvinen@linux.intel.com>
Add Bartlett Lake P-core only product support to intel_pmc_core
driver. Bartlett Lake hybrid product reuses Raptor Lake model name
so it is already enabled.

Acked-by: Xi Pardee <xi.pardee@linux.intel.com>
Signed-off-by: Li Yifan <yifan2.li@intel.com>
Link: https://lore.kernel.org/r/20250826034550.2284738-1-yifan2.li@intel.com
Reviewed-by: Ilpo Järvinen <ilpo.jarvinen@linux.intel.com>
Signed-off-by: Ilpo Järvinen <ilpo.jarvinen@linux.intel.com>
asus_wmi_register_driver() may be called from multiple drivers
concurrently, which can lead to the racy list operations, eventually
corrupting the memory and hitting Oops on some ASUS machines.
Also, the error handling is missing, and it forgot to unregister ACPI
lps0 dev ops in the error case.

This patch covers those issues by introducing a simple mutex at
acpi_wmi_register_driver() & *_unregister_driver, and adding the
proper call of asus_s2idle_check_unregister() in the error path.

Fixes: feea7bd6b0 ("platform/x86: asus-wmi: Refactor Ally suspend/resume")
Link: https://bugzilla.suse.com/show_bug.cgi?id=1246924
Link: https://lore.kernel.org/07815053-0e31-4e8e-8049-b652c929323b@kernel.org
Signed-off-by: Takashi Iwai <tiwai@suse.de>
Link: https://lore.kernel.org/r/20250827052441.23382-1-tiwai@suse.de
Reviewed-by: Ilpo Järvinen <ilpo.jarvinen@linux.intel.com>
Signed-off-by: Ilpo Järvinen <ilpo.jarvinen@linux.intel.com>
Prevents instant wakeup ~1s after suspend.

It seems to be kernel/system dependent if the IRQ actually manages to wake
the system every time or if it gets ignored (and everything works as
expected).

Signed-off-by: Christoffer Sandberg <cs@tuxedo.de>
Signed-off-by: Werner Sembach <wse@tuxedocomputers.com>
Cc: stable@vger.kernel.org
Link: https://lore.kernel.org/r/20250827131424.16436-1-wse@tuxedocomputers.com
Reviewed-by: Ilpo Järvinen <ilpo.jarvinen@linux.intel.com>
Signed-off-by: Ilpo Järvinen <ilpo.jarvinen@linux.intel.com>
* there is a dedicated "noise cancel" key in top row, between mic mute
  and PrintScreen; it sends 0xCA when pressed by itself (mapped to F13),
  0xCB with Fn (mapped to F14)
* Fn+f sends 0x9D; it is not documented in the manual, but some web
  search results mention "asus intelligent performance"; mapped to FN_F

Signed-off-by: Anton Khirnov <anton@khirnov.net>
Reviewed-by: Hans de Goede <hansg@kernel.org>
Link: https://lore.kernel.org/r/20250827152954.4844-1-anton@khirnov.net
Reviewed-by: Ilpo Järvinen <ilpo.jarvinen@linux.intel.com>
Signed-off-by: Ilpo Järvinen <ilpo.jarvinen@linux.intel.com>
Deny all sampling event by the CPUMF counter facility device driver
and return -ENOENT. This return value is used to try other PMUs.
Up to now events for type PERF_TYPE_HARDWARE were not tested for
sampling and returned later on -EOPNOTSUPP. This ends the search
for alternative PMUs. Change that behavior and try other PMUs
instead.

Fixes: 613a41b0d1 ("s390/cpum_cf: Reject request for sampling in event initialization")
Acked-by: Sumanth Korikkar <sumanthk@linux.ibm.com>
Signed-off-by: Thomas Richter <tmricht@linux.ibm.com>
Signed-off-by: Alexander Gordeev <agordeev@linux.ibm.com>
Each PAI PMU device driver returns -EINVAL when an event is out of
its accepted range. This return value aborts the search for an
alternative PMU device driver to handle this event.
Change the return value to -ENOENT. This return value is used to
try other PMUs instead.  This makes the PMUs more robust when
the sequence of PMU device driver initialization changes (at boot time)
or by using modules.

Fixes: 39d62336f5 ("s390/pai: add support for cryptography counters")
Acked-by: Sumanth Korikkar <sumanthk@linux.ibm.com>
Signed-off-by: Thomas Richter <tmricht@linux.ibm.com>
Signed-off-by: Alexander Gordeev <agordeev@linux.ibm.com>
Add a new command line option --no_ublk_fixed_fd that excludes the ublk
control device (/dev/ublkcN) from io_uring's registered files array.
When this option is used, only backing files are registered starting
from index 1, while the ublk control device is accessed using its raw
file descriptor.

Add ublk_get_registered_fd() helper function that returns the appropriate
file descriptor for use with io_uring operations.

Key optimizations implemented:
- Cache UBLKS_Q_NO_UBLK_FIXED_FD flag in ublk_queue.flags to avoid
  reading dev->no_ublk_fixed_fd in fast path
- Cache ublk char device fd in ublk_queue.ublk_fd for fast access
- Update ublk_get_registered_fd() to use ublk_queue * parameter
- Update io_uring_prep_buf_register/unregister() to use ublk_queue *
- Replace ublk_device * access with ublk_queue * access in fast paths

Also pass --no_ublk_fixed_fd to test_stress_04.sh for covering
plain ublk char device mode.

Signed-off-by: Ming Lei <ming.lei@redhat.com>
Link: https://lore.kernel.org/r/20250827121602.2619736-3-ming.lei@redhat.com
Signed-off-by: Jens Axboe <axboe@kernel.dk>
When running test_stress_04.sh, the following warning is triggered:

WARNING: CPU: 1 PID: 135 at drivers/block/ublk_drv.c:1933 ublk_ch_release+0x423/0x4b0 [ublk_drv]

This happens when the daemon is abruptly killed:

- some references may still be held, because registering IO buffer
doesn't grab ublk char device reference

OR

- io->task_registered_buffers won't be cleared because io buffer is
released from non-daemon context

For zero-copy and auto buffer register modes, I/O reference crosses
syscalls, so IO reference may not be dropped naturally when ublk server is
killed abruptly. However, when releasing io_uring context, it is guaranteed
that the reference is dropped finally, see io_sqe_buffers_unregister() from
io_ring_ctx_free().

Fix this by adding ublk_drain_io_references() that:
- Waits for active I/O references dropped in async way by scheduling
  work function, for avoiding ublk dev and io_uring file's release
  dependency
- Reinitializes io->ref and io->task_registered_buffers to clean state

This ensures the reference count state is clean when ublk_queue_reinit()
is called, preventing the warning and potential use-after-free.

Fixes: 1f6540e2aa ("ublk: zc register/unregister bvec")
Fixes: 1ceeedb597 ("ublk: optimize UBLK_IO_UNREGISTER_IO_BUF on daemon task")
Fixes: 8a8fe42d76 ("ublk: optimize UBLK_IO_REGISTER_IO_BUF on daemon task")
Signed-off-by: Ming Lei <ming.lei@redhat.com>
Link: https://lore.kernel.org/r/20250827121602.2619736-2-ming.lei@redhat.com
Signed-off-by: Jens Axboe <axboe@kernel.dk>
Having setup time 0 violates tAR, tCLR of some chips, for instance
TOSHIBA TC58NVG2S3ETAI0 cannot be detected successfully (first ID byte
being read duplicated, i.e. 98 98 dc 90 15 76 14 03 instead of
98 dc 90 15 76 ...).

Atmel Application Notes postulated 1 cycle NRD_SETUP without explanation
[1], but it looks more appropriate to just calculate setup time properly.

[1] Link: https://ww1.microchip.com/downloads/aemDocuments/documents/MPU32/ApplicationNotes/ApplicationNotes/doc6255.pdf

Cc: stable@vger.kernel.org
Fixes: f9ce2eddf1 ("mtd: nand: atmel: Add ->setup_data_interface() hooks")
Signed-off-by: Alexander Sverdlin <alexander.sverdlin@siemens.com>
Tested-by: Alexander Dahl <ada@thorsis.com>
Signed-off-by: Miquel Raynal <miquel.raynal@bootlin.com>
In case OOB write is requested during a data write, ECC is currently
lost. Avoid this issue by only writing in the free spare area.
This issue has been seen with a YAFFS2 file system.

Signed-off-by: Christophe Kerello <christophe.kerello@foss.st.com>
Cc: stable@vger.kernel.org
Fixes: 2cd457f328 ("mtd: rawnand: stm32_fmc2: add STM32 FMC2 NAND flash controller driver")
Signed-off-by: Miquel Raynal <miquel.raynal@bootlin.com>
If a ma35_nand_chip_init() call fails, then a reference to 'nand_np' still
needs to be released.

Use for_each_child_of_node_scoped() to fix the issue.

Fixes: 5abb5d414d ("mtd: rawnand: nuvoton: add new driver for the Nuvoton MA35 SoC")
Signed-off-by: Christophe JAILLET <christophe.jaillet@wanadoo.fr>
Signed-off-by: Miquel Raynal <miquel.raynal@bootlin.com>